Know every script on your site, what it costs, and who owns it.
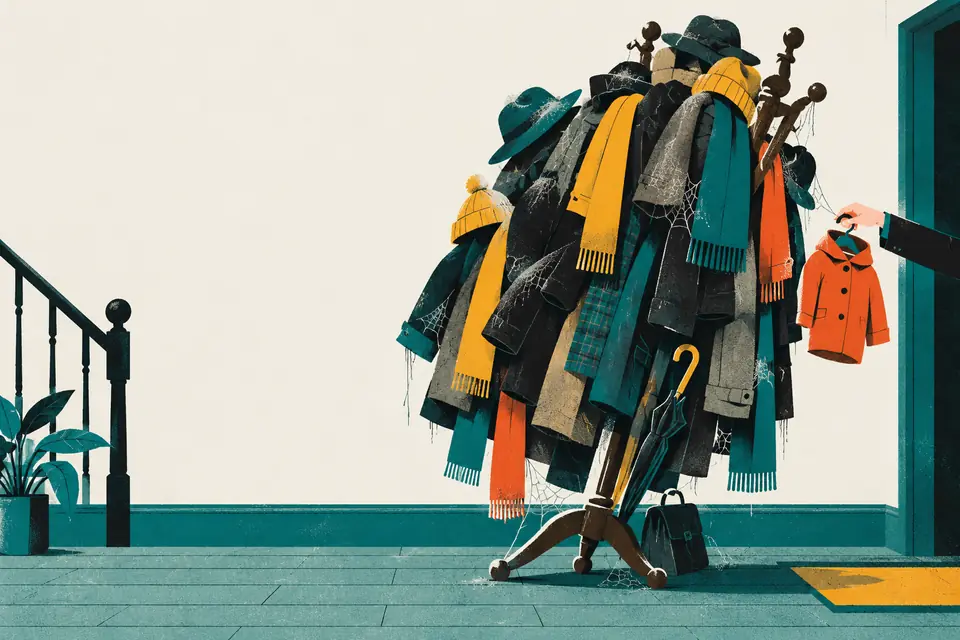
Tags pile up like coats on a hall stand: a pixel from a campaign that ended years ago, a heatmap nobody checks, a chat widget on pages that don't need it. We find every third-party script, measure what it costs your visitors, check when it fires relative to consent, and give each one an owner.
Most sites run scripts nobody remembers approving
Third-party scripts arrive one request at a time. Marketing adds a pixel for a campaign. A vendor's support widget goes on every page. An agency installs a heatmap tool for a redesign. Years later the campaign is over, the agency is gone, and the scripts still run on every visit.
Each one has a cost. It downloads bytes, competes for the main thread, and can delay the response to a tap or key press, which hurts Interaction to Next Paint and makes the page feel sluggish to keyboard and screen-reader users. Many also send data about your visitors to domains no one on your team has reviewed, sometimes before the visitor has answered your consent banner.
Tag governance answers four questions for every script: what is it, what does it cost, when does it fire, and who is responsible for it.
What we record for every script
The inventory covers tags in your tag manager, scripts hard-coded in templates, and everything those scripts load in turn.
| Field | How we measure it | Why it matters |
|---|---|---|
| Vendor and purpose | Network logs, tag manager containers, and vendor documentation | You can't decide about a script until you know what it's for |
| Cost | Bytes transferred and main-thread milliseconds, from performance traces on a throttled mobile profile | Shows which scripts slow loading and interactions the most |
| Timing relative to consent | Network captures with no choice made, after rejecting, and after accepting | Reveals tags that fire before, or despite, the visitor's choice |
| Data destinations | Every domain each script sends requests to, including scripts it loads itself | Tells your privacy team who receives data about your visitors |
| Owner and last use | Interviews, tag manager history, and whether anyone still reads the data | Finds abandoned tags nobody will miss |
| Decision | Agreed with the owner | Keep, delay, consolidate, replace, or remove |
Two state laws now shape how your tags should behave
The Kentucky Consumer Data Protection Act took effect on January 1, 2026. It generally covers businesses that control or process the personal data of 100,000 or more Kentucky consumers in a calendar year, or 25,000 for businesses that get more than half of their revenue from selling personal data, and it gives consumers the right to opt out of targeted advertising and the sale of their data. The Kentucky Attorney General enforces it, there is no private right of action, and a business gets a cure period of 30 days after written notice.
California moved in a different direction. SB 690, signed on September 30, 2026, ends private lawsuits over website and app tracking under the pen-register provisions of the California Invasion of Privacy Act (CIPA) from January 1, 2027, leaving those claims to the Attorney General. It also applies to pending pen-register claims in cases filed on or after January 1, 2025. It does not end private CIPA claims for wiretapping or eavesdropping, which plaintiffs can still bring.
Neither law tells you which tags to keep. Both make it more important to know what your tags do and when. We provide technical evidence, not legal advice; what these laws require of you is a question for your attorney.
What changes when every tag has an owner
Without governance
- Anyone with publish rights in the tag manager can add a script to every page
- Pixels load on page view, before the consent banner is answered
- Tags from finished campaigns keep running for years
- Nobody knows what a script costs until the site feels slow
With governance
- Every tag has a named owner, a purpose, and a review date
- Consent-dependent tags wait for a recorded choice, verified in network logs
- A quarterly review retires tags their owners no longer need
- A third-party budget caps main-thread time, and a Content Security Policy blocks unapproved domains
How the audit runs
Capture
We load your key templates in three consent states, with no choice made, after rejecting, and after accepting, on a throttled mobile profile, and record every request and a performance trace.
Attribute
We tie each request and each millisecond of main-thread time to a script, a vendor, and a tag manager entry, including scripts loaded by other scripts.
Find the owners
We work with marketing, analytics, and IT to name an owner for every tag and confirm whether anyone still uses its data.
Decide and clean up
Owners choose to keep, delay, consolidate, replace, or remove. We can make the changes ourselves and tidy the tag manager's workspaces, naming, triggers, and publish permissions.
Lock it in
We set up an approval process, a Content Security Policy that starts in report-only mode, and script-change alerts through Baclion Watch.
A fixed-scope audit
Tag & Script Governance audit
Starting at
$3,600
An inventory of every third-party script, its cost in milliseconds, and when it fires relative to consent.
Request a quoteImplementation in your tag manager or consent platform is quoted after the audit, once you've decided what stays.
Questions from marketing, IT, and privacy teams
Is this a privacy law review?
No. It's a technical audit of what each tag does, what it costs, and when it fires. Your attorney or privacy team decides what the law requires, and we give them evidence to decide with.
Will removing tags break our analytics?
Not if it's done in order. We confirm each owner's needs first, remove duplicates and dead tags, and test the remaining measurement before and after each change.
Which tag managers and consent tools do you work with?
We work in Google Tag Manager and other common tag managers, and with the widely used consent management platforms. The method doesn't depend on the tool: capture the network, attribute the cost, verify the consent behavior.
What is a Content Security Policy, and do we need one?
It's an HTTP header that tells the browser which domains may run scripts on your pages, so unapproved scripts are blocked, including ones injected through a compromised vendor. We start it in report-only mode, so nothing breaks while you learn what's running.
Keep reading
Tell us what your website needs to do.
Send a link and a sentence about your deadline. You will hear back from a person within one business day, usually with a short list of questions and a proposed scope.